What Most Liveness Vendors Get Wrong About Deepfake Defence
Author: admin | 13 Mar 2026In This Post
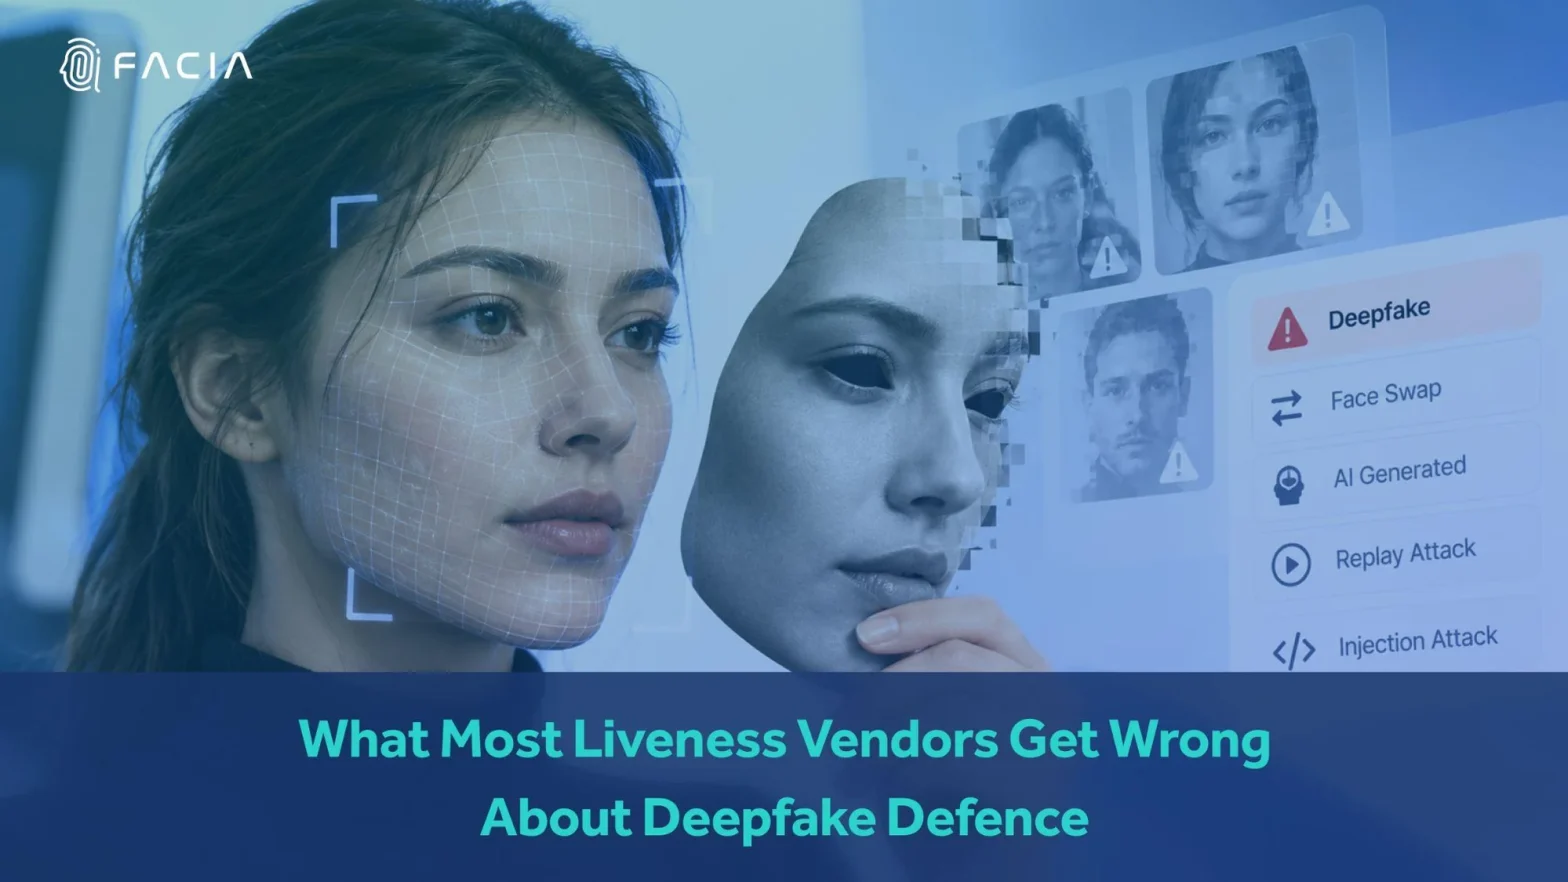
A liveness check can pass while a deeper identity attack slips through. That is the challenge when businesses compare liveness vendors for deepfake defence. Traditional liveness detection may catch printed photos, replayed videos, or masks. Modern fraud can enter through synthetic faces, virtual cameras, manipulated streams, or injected biometric data before a conventional liveness decision.
The detection problem is also harder than headline accuracy suggests. A 2025 systematic review found that only 46.3% of the selected publications supported the ability of deepfake detection techniques to generalise across different types of deepfakes. The researchers also identified overfitting to known datasets as a key obstacle when models face unseen manipulations.
For buyers, this shifts the focus from “Does the vendor offer liveness?” to “What exactly does the vendor detect, where does detection happen, and how well does it hold up when the attack changes?” A badge or benchmark is useful, but only when buyers understand what sits behind it.
Liveness Detection for Deepfake Defence: What Buyers Should Evaluate
Presentation Attack Detection, or PAD, focuses on attacks presented to a biometric capture device, including printed images, replayed videos, masks, and screens.
Deepfake injection attacks can take many forms, including virtual cameras, manipulated video feeds, pre-recorded biometric data, and synthesised facial media.
NIST’s digital identity guidance calls for PAD in facial recognition deployments and requires an Impostor Attack Presentation Accept Rate of less than 0.07 for deployment testing. In addition, NIST suggests verifying sensor and endpoint integrity to increase the likelihood of finding an injection attack. The test scope is as important as the result.
Five Questions That Reveal a Liveness Vendor’s Real Coverage
1. What Exactly Does Your Certification Cover?
Certification is useful only when its scope is clear. Ask which product version was tested, which devices were included, and which metrics were reported.
If a vendor mentions ISO/IEC 30107-3 or independent PAD testing, ask if it is specific to presentation attacks.
Then request support for statements about deepfakes and injection attacks. Don’t mistake a PAD result for protection against synthetic media or manipulated capture streams.
Ask for the SDK version tested, device coverage, attack scope and data from any relevant APCER and BPCER.
2. Where Is an Injected Feed Detected?
An injection attack may attempt to replace what the camera sends.
Can the system identify a virtual camera? Can it detect a prerecorded or manipulated stream? Does protection begin on the device or only after biometric data reaches the backend?
“Deepfakes” aren’t a matter of which camera you use: a statement like “we detect deepfakes” doesn’t clarify what happens when synthetic media isn’t captured on the actual camera.
Security teams must understand how the capture layer, device environment, and server-side analysis work together. See How Deepfakes Are Used to Bypass KYC Onboarding: A Technical Breakdown of the technical attack flow.
3. How Current Is the Deepfake Detection Model?
Deepfake detection depends on what a model has learned.
A detector can respond well to manipulations it is familiar with and differently to a new generator/editing technique.
Inquire about the last time the model was updated, if there are unseen generators being used to test it, and how often it is revalidated.
4. Can the Vendor Prove Performance Beyond Controlled Testing?
Controlled testing creates repeatable conditions. Real identity verification does not.
Users use different compression, lighting, and devices. Attackers introduce foreign generators, virtual cameras, and manipulated streams.
Request evidence from various datasets, devices, low-light, compressed video, and new attack generators.
PAD testing reveals performance against predefined presentation attacks. Is the detection spectrum reliable even when conditions change?
Check out How Biometric Liveness Detection Prevents Deepfakes to learn more about the detection layer.
5. What Is the Independently Verified False Acceptance Rate?
“High accuracy” is hard to interpret on its own.
Request the False Acceptance Rate (FAR) and explain what is meant by it. What version of the product was tested? What was the threshold used? Has it been checked independently? What was the type of attack it measured?
The same applies to FRR, APCER, and BPCER. A percentage has limited value if buyers don’t know which part of the verification process it measures.
A Practical Liveness Vendor Evaluation Scorecard
| Evaluation Area | Weak Evidence | Moderate Evidence | Strong Evidence |
| Certification scope | Badge only | Valid certification | Scope, version, attacks, metrics documented |
| Injection protection | No explanation | Protection claimed | Architecture and testing evidence |
| Model freshness | Update cycle unclear | Regular updates claimed | Update and validation process documented |
| Real-world performance | Internal benchmark | Limited external testing | Cross-dataset and unseen-attack evidence |
| Error metrics | Generic accuracy | FAR or FRR supplied | FAR, FRR, APCER, BPCER explained |
The scorecard shows where deeper review is needed.
Lab Testing vs. Real-World Deepfake Detection Performance
Lab testing is valuable because repeatable conditions make results easier to compare. Problems arise when one result is treated as proof against every biometric attack.
Defence against deepfakes is an ever-evolving battle. New generators are emerging, compression changes visual signals, and attackers keep improving synthetic media. Detectors may also encounter techniques they never saw in their training set.
A strong PAD result can signal resistance to defined presentation attacks. Cross-dataset and unseen-generator testing answers another question: Can detection hold up in an unknown (and unfamiliar) benchmark?
Research on deepfake generalisation validates this distinction. Buyers should view strong performance as a positive sign, but not a guarantee of deepfake resilience.
What a Complete Deepfake Defence Stack Should Cover
Successful biometric security requires security touchpoints throughout the identity journey.
Presentation attack detection (PAD) deals with physical spoofs at the camera.
The study of synthetic or manipulated facial media is deepfake detection. Injection attack protection relies on maintaining integrity when virtual cameras or streams have been altered.
Identity is verified using trusted biometrics to confirm it is the same person.
These controls are wired but not switchable. Vendors provide information about location(s) and evidence to support locations.
How Facia Addresses Gaps in Liveness and Deepfake Defence
Choosing a liveness provider comes down to whether its protection matches the risks a real identity verification flow can face. Presentation attacks, synthetic media, injected feeds, and identity mismatch target different parts of that journey, so one biometric check can leave gaps.
Facia addresses these risks across the verification process. DeepLiveness helps confirm genuine presence while identifying sophisticated spoofing attempts. When the threat is synthetic or manipulated facial media, Deepfake Detection examines the content for signs of manipulation. If an attacker tries to bypass trusted capture through a virtual camera or altered stream, Injection Attack Protection helps identify that interference earlier in the flow. Once the biometric input is trusted, Face Verification confirms that the person matches the identity being claimed.
This gives businesses a connected approach to liveness detection and deepfake defence, covering capture integrity, media authenticity, and identity matching.
Strengthen your identity verification against spoofing, deepfakes, and injection attacks. Book a demo with Facia today.